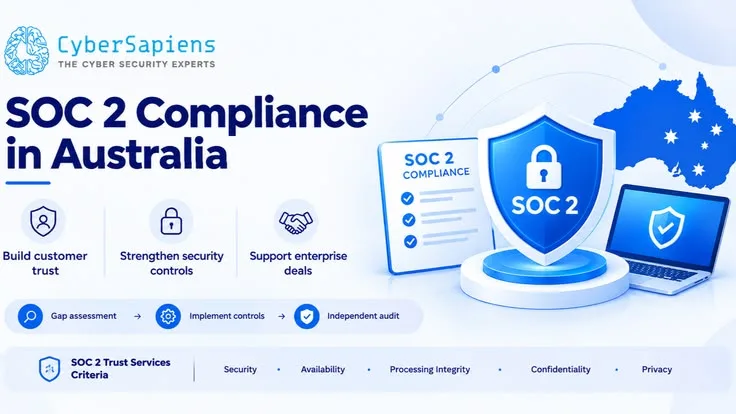
Quick answer: Not by law, but often by deal. SOC 2 is not legally mandated in Australia. Demand comes from enterprise buyers, especially in the US, who treat a current SOC 2 report as a requirement in vendor due diligence. If your customers are asking for it, or your sales team is losing time to security questionnaires, it is time to plan. A specialist team can guide SOC 2 compliance in Australia from readiness through to the final report.
Why this catches teams off guard
Many Australian tech companies grow without needing formal assurance. Then a US prospect reaches the security review stage and asks, “Can you share your SOC 2 report?”
If the answer is no, the deal usually stalls. The timeline surprises teams most. A Type 1 report can take 6-8 weeks, but a Type 2 report needs months of observed evidence that cannot be created after the fact. Starting after the request arrives means starting behind.
A seven-step check before you start SOC 2
- Confirm the trigger. Identify who is asking and why, whether it is a named prospect, a renewal, or a regulated customer.
- Define the scope. List the systems, data, people, and vendors that support the service you sell.
- Choose the criteria. Security is mandatory. Add Availability, Processing Integrity, Confidentiality, or Privacy only if your customers need them.
- Pick the report type. Type 1 tests control design at a point in time. Type 2 tests how controls operate over 3-12 months.
- Run a gap assessment. Map your current controls to the Trust Services Criteria and list what is missing.
- Reuse what you have. An existing ISO 27001 programme typically covers 60-70% of SOC 2 controls, which cuts both cost and time.
- Choose your audit route. Options include a Big 4 firm, an overseas audit firm you manage yourself, or a local consultancy working with an audit partner.
Step 4 is where expectations most often go wrong. No provider can shorten the Type 2 observation window, so be cautious about any “Type 2 in 45 days” claim.
Evidence auditors typically request
SOC 2 is an attestation report issued after an independent audit, not a certificate. The auditor tests whether your controls exist and, for Type 2, whether they ran consistently. Typical requests include:
- Access records: user provisioning, offboarding, and periodic access reviews, in line with SOC 2 access control requirements.
- Risk and policy documents: an approved risk assessment and signed-off security policies.
- Change management: tickets and approvals showing how code and infrastructure changes are reviewed.
- Incident response: the plan, plus proof it was tested or used.
- Vendor oversight: assessments of the third parties that touch your data.
- People controls: background checks where applicable and security awareness training records.
- Resilience: backup and disaster recovery testing.
For Type 2, samples are drawn from across the whole observation period. That is why evidence collection has to start on day one. Our SOC 2 compliance checklist is a practical place to start.
Building a SOC 2 programme that lasts
Auditors want a repeatable, owned process, not a one-off sprint. A workable programme has five parts:
- Scope and ownership. Document the systems in scope and name one accountable owner.
- Policies and controls. Write policies you actually follow, and map each to a control.
- Evidence collection. Decide what is automated and what stays manual, and collect it continuously.
- Monitoring and internal review. Review controls regularly so gaps surface before the auditor finds them.
- Annual renewal. Treat SOC 2 as a yearly cycle, with reviews after major changes to your systems or vendors.
If you already hold or plan to pursue ISO 27001, build the two together. One control set can support both, which is useful if you sell into the US as well as Europe or APAC. See our ISO 27001 certification service in Australia.
Frequently asked questions
Is SOC 2 legally required in Australia?
No. Demand is commercial, driven by enterprise buyers who want proof that vendors protect their data.
Is SOC 2 a certification?
Technically no. It is an attestation report from an independent audit firm. “SOC 2 certification” is common shorthand, but buyers ask for the report itself.
How long does SOC 2 take?
A Type 1 report typically takes 6-8 weeks if controls already exist. A Type 2 report typically takes 9-12 months from a standing start, including the observation window.
Do we need Type 1 before Type 2?
No. Many companies go straight to Type 2. Type 1 is useful as a short bridge when a deal is under time pressure.
Does ISO 27001 help with SOC 2?
Yes. The two frameworks share an estimated 60-70% of controls, so existing ISO 27001 work reduces SOC 2 effort. We also publish a guide to SOC 2 cost in Australia.
Who issues the SOC 2 report?
A licensed audit firm. Australian companies typically use a Big 4 firm, an overseas specialist, or a local consultancy working with an audit partner.
Not sure where you stand?
List who has asked for SOC 2, compare your current controls with the evidence above, and close the gaps before your audit window opens. Book a free SOC 2 consultation for a fixed-price quote.